AI Governance
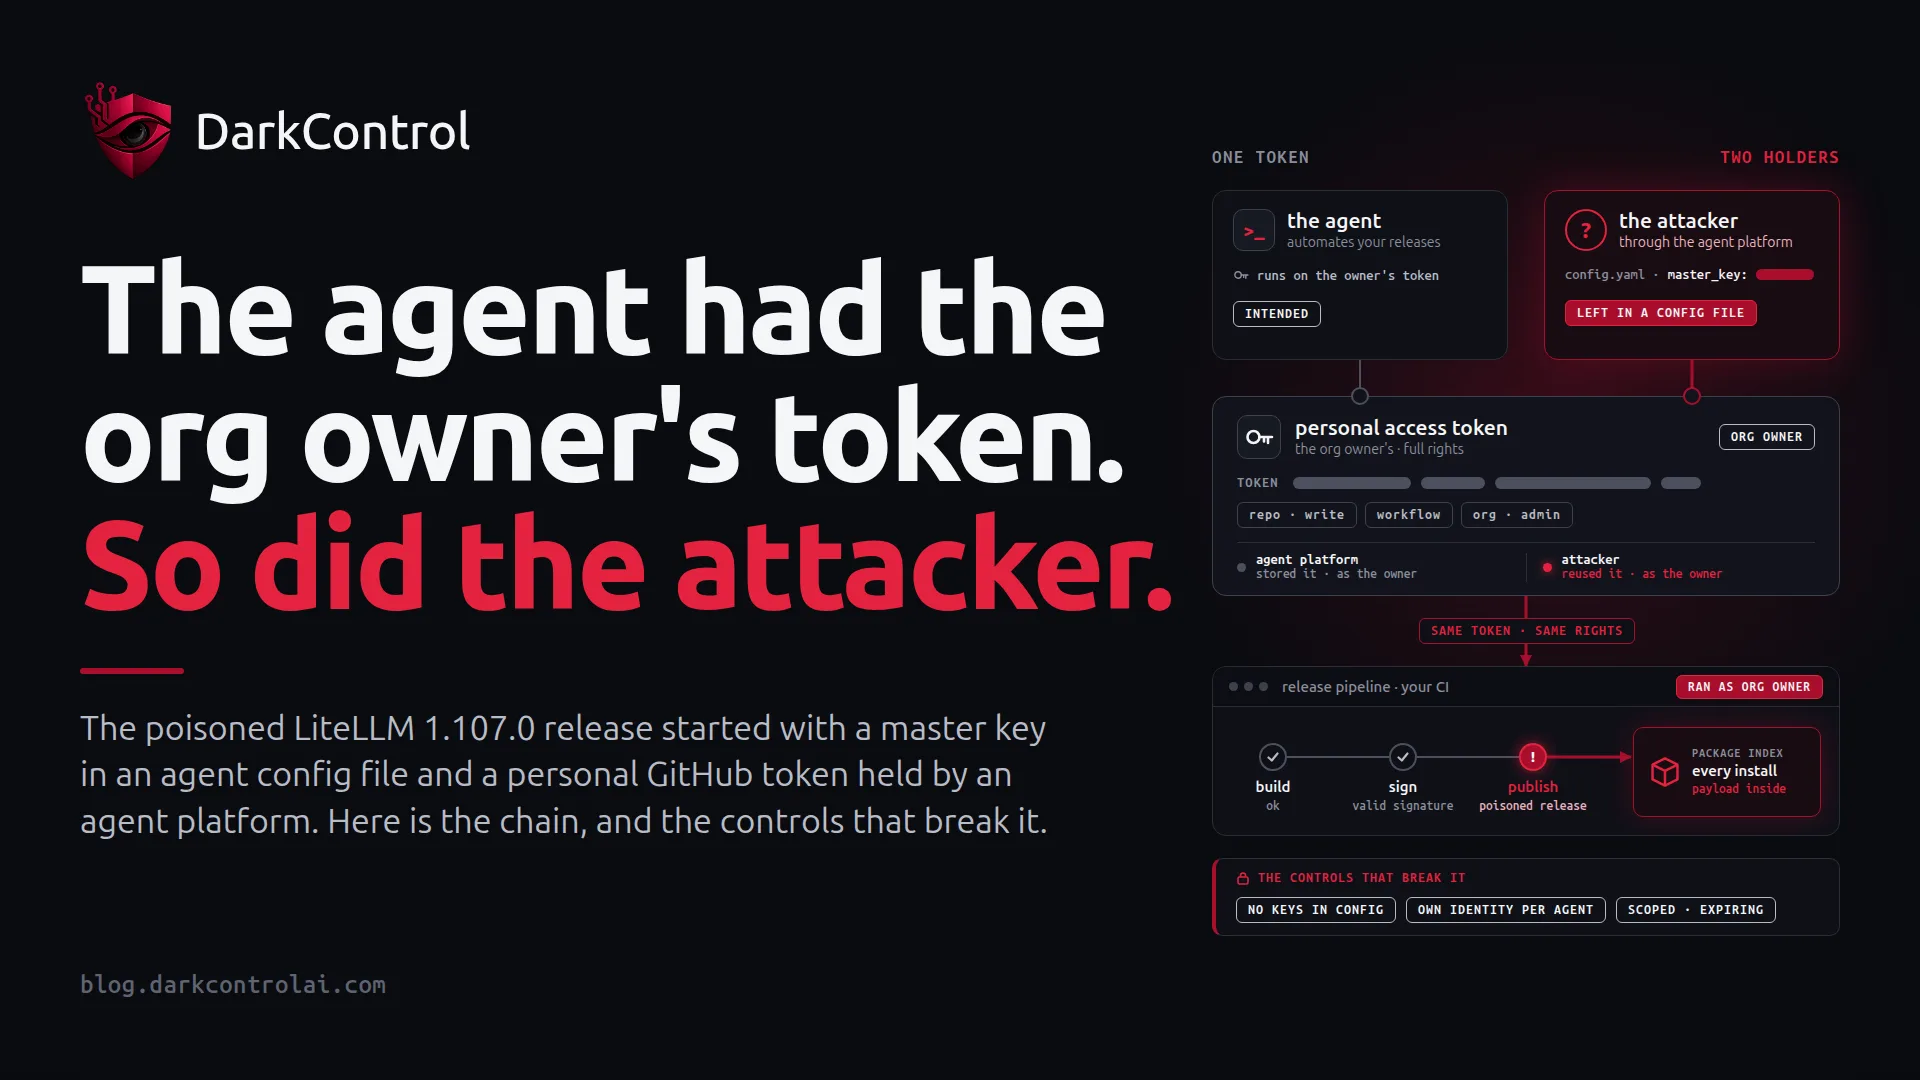
The agent had the org owner's token. So did the attacker.
On 21 October a credential-stealing LiteLLM 1.107.0 reached PyPI and Docker. LiteLLM traces it to a master key in a committed agent config file and an unscoped owner token held by an agent platform. What happened, and the controls that break the chain.
·6 min read